Splunk expertise
We work across the full lifecycle of a Splunk platform: licensing, complex and hybrid architectures, Enterprise Security, SOAR automation, application development, cost optimisation and turning data into value.
Anatomy of an engagement
Audit
We measure the real state of the platform: architecture, indexer health, volumes, source quality, ingestion cost. The deliverable is a list of actions ordered by payoff.
Architecture
Designing or reworking the architecture, on-premise, cloud or hybrid. Log normalisation, migration from another SIEM, integration with existing tooling.
Enterprise Security
Implementing and tuning ES: detection use cases mapped to MITRE ATT&CK, noise reduction, alert quality over alert volume.
Automation and development
SOAR playbooks, custom Splunk applications, business-oriented dashboards, automation of repetitive operational work.
The applications we build
We develop and publish our own Splunk applications. They are publicly available on Splunkbase, installable by any organisation.
Process-IT Add-on for Cyberwatch (opens in a new window)
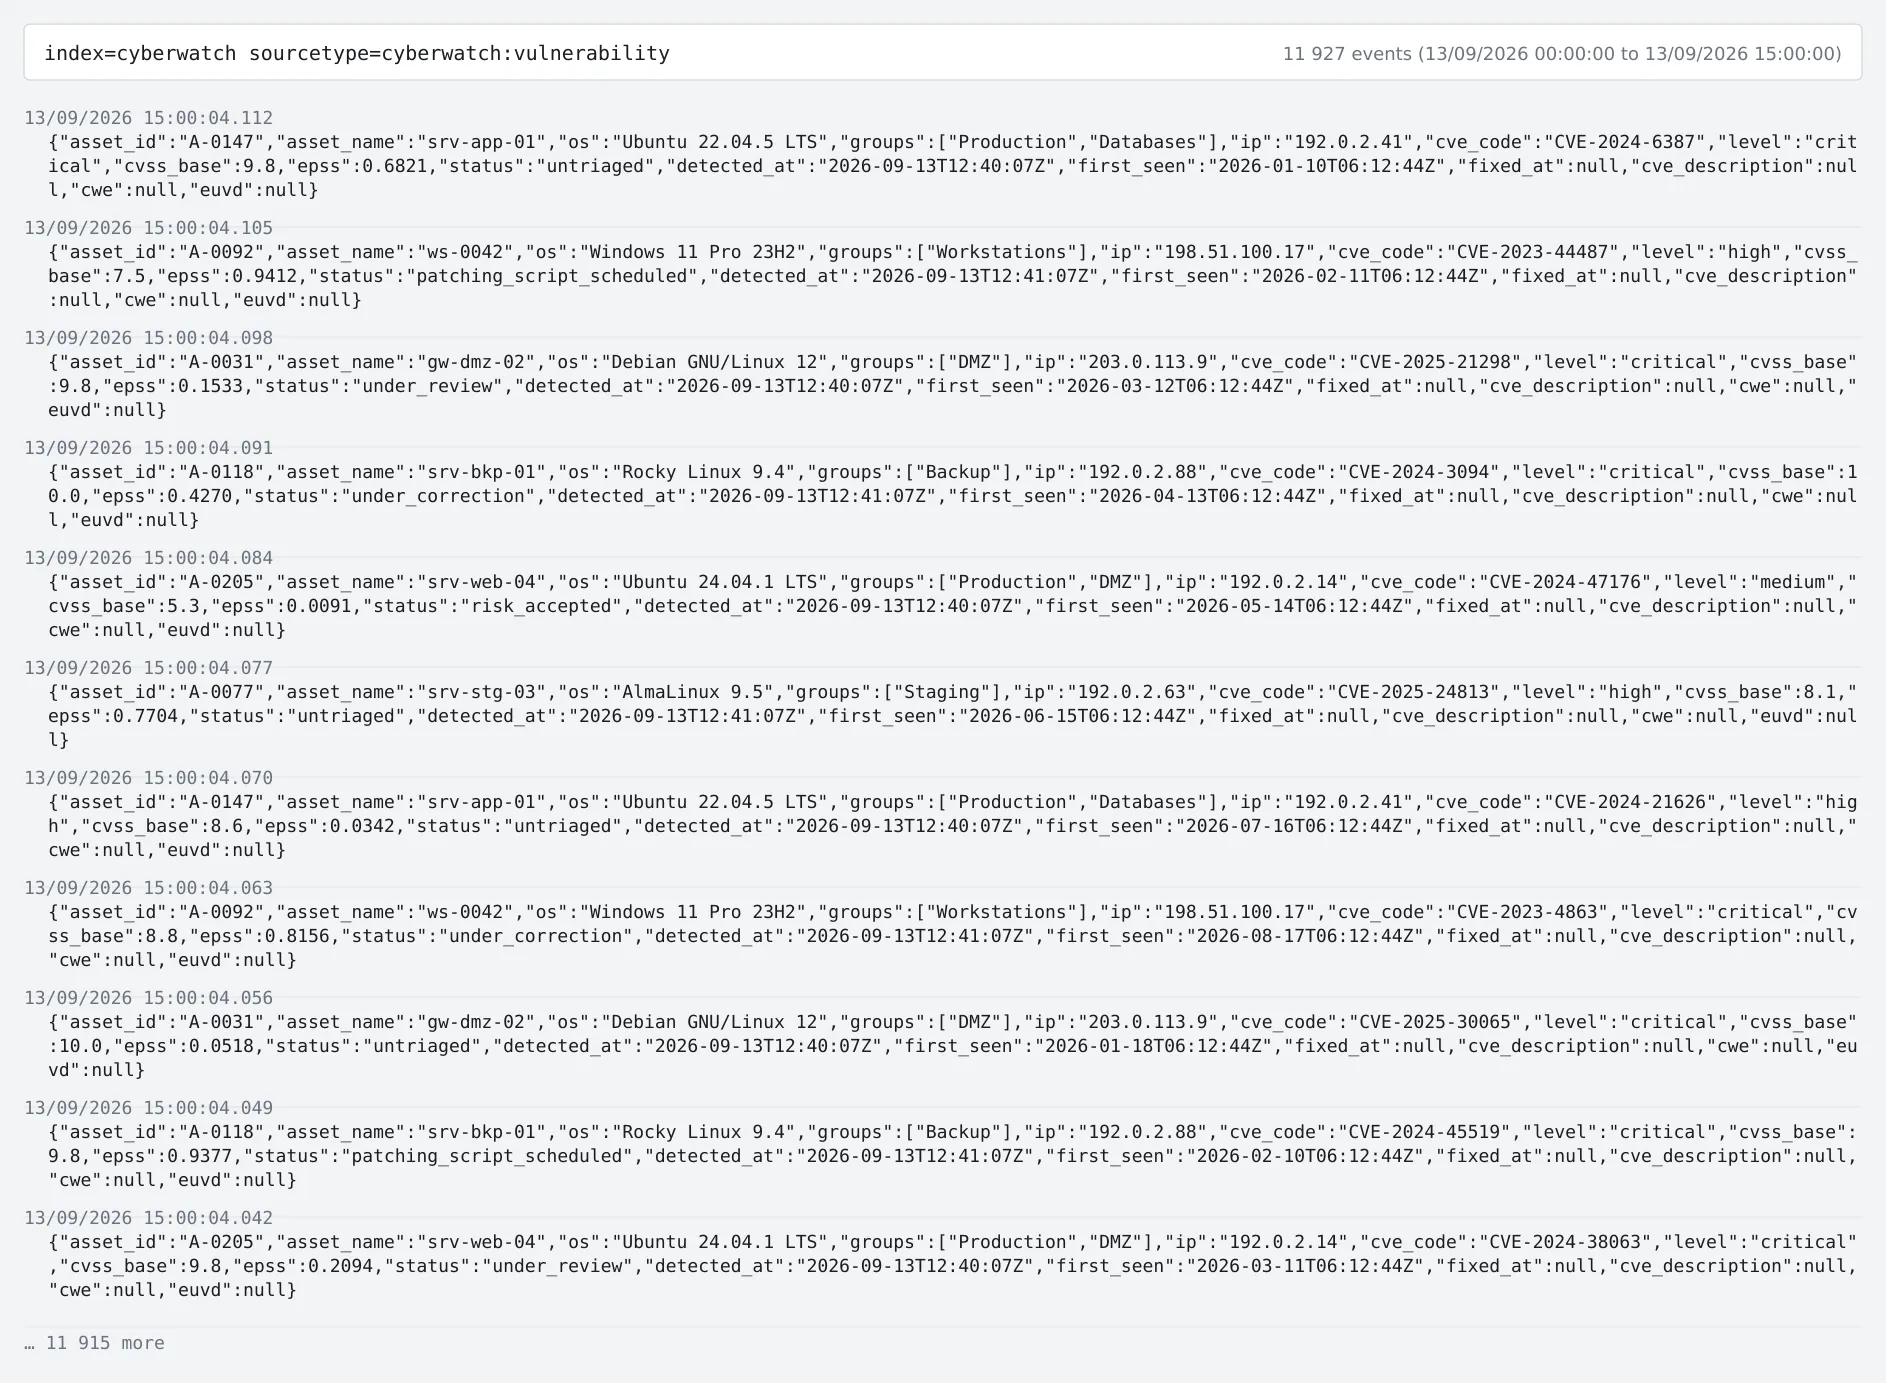
Collection from the Cyberwatch API: assets, vulnerabilities, compliance, incidents. CIM-normalised to the Vulnerabilities data model.
Process-IT App for Cyberwatch (opens in a new window)
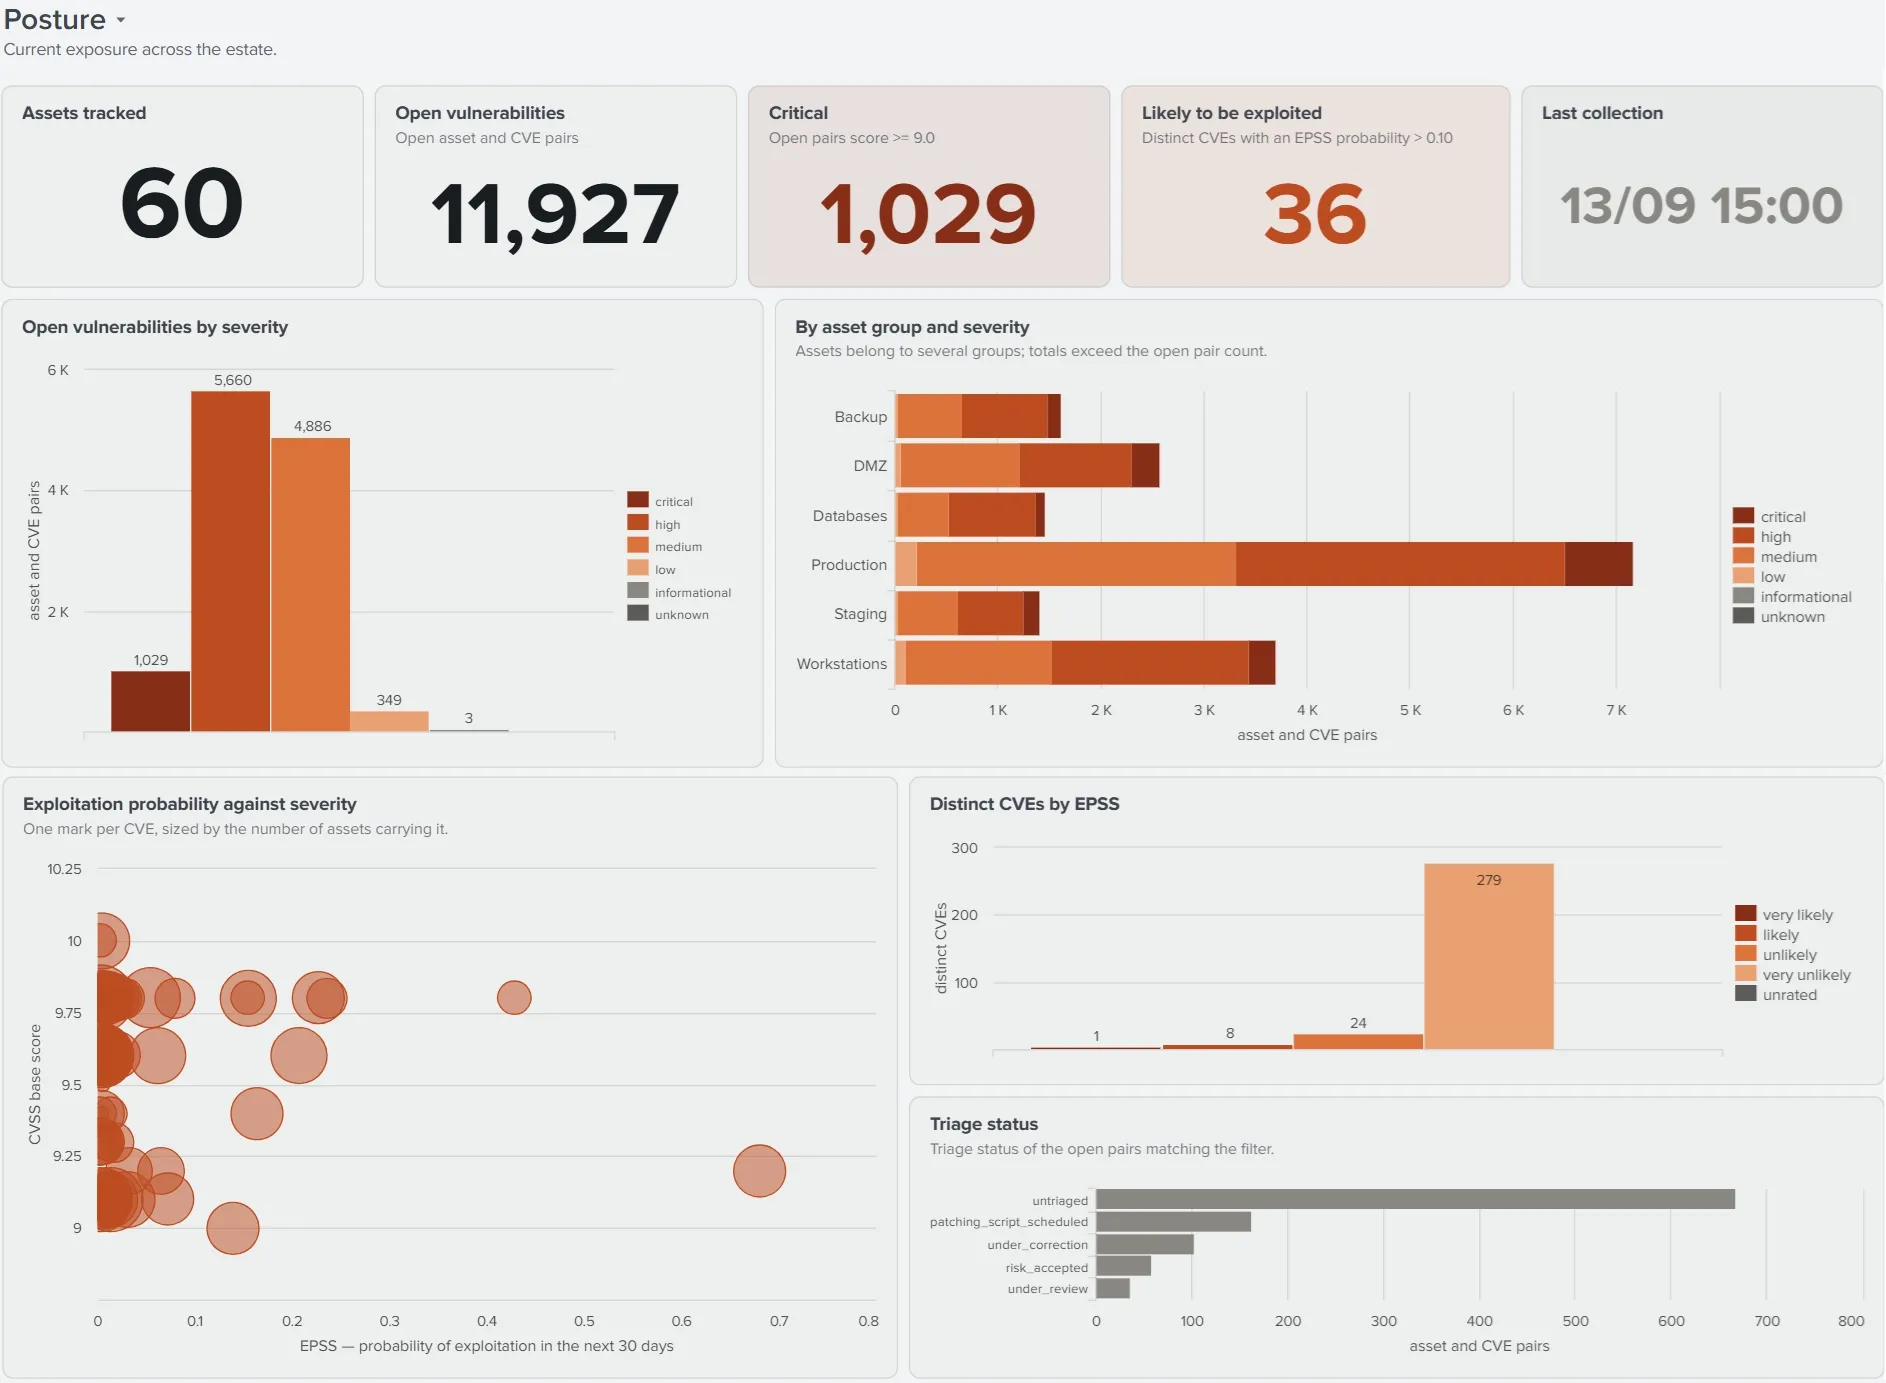
Ten dashboards: exposure, remediation priority, compliance, inventory, collection health.
Process-IT Add-on for Stormshield (opens in a new window)
Stormshield firewall syslog: event breaking, field extraction, CIM compliance. A dozen categories, each mapped to its data model.
Before / after